Bitget Says $351.6M Hack Used Spoofed Transfers, Not Stolen Private Keys
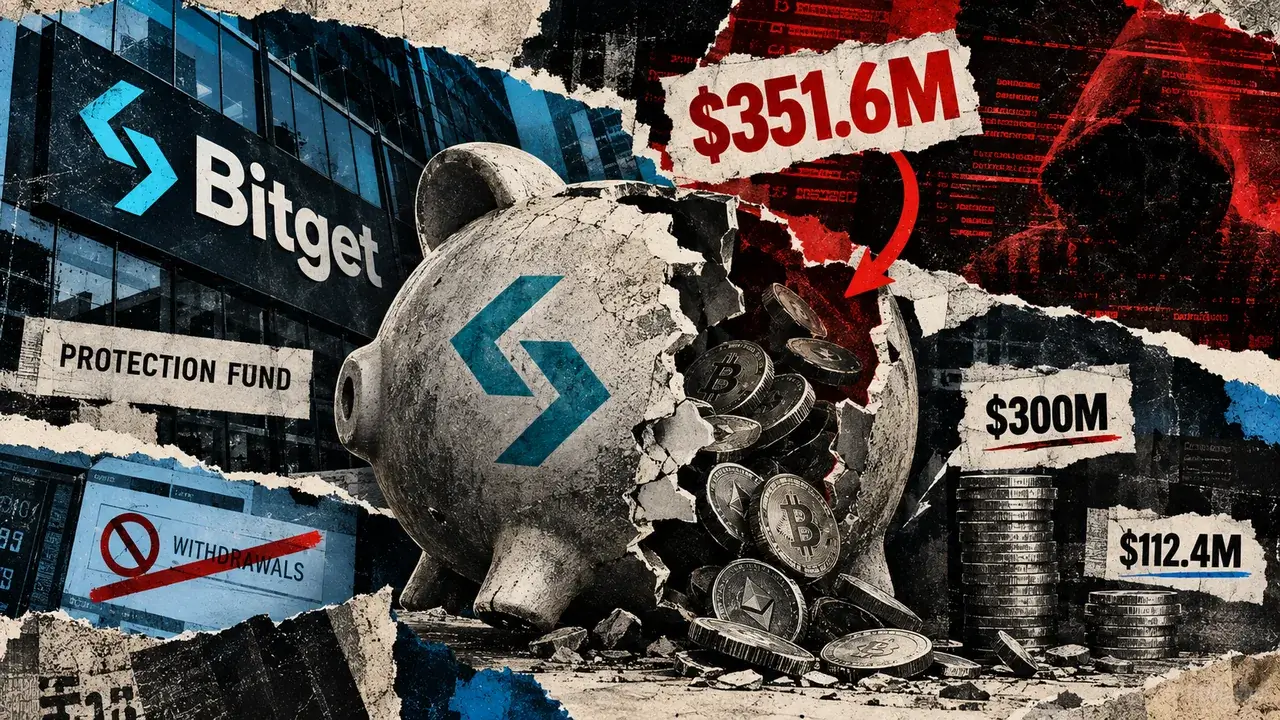
Attackers drained $351.6 million from Bitget after compromising a wallet backend and spoofing transaction data. Withdrawals remain suspended, while the exchange says its protection fund will cover the loss.

Bitget lost $351.6 million after attackers breached a backend system in its wallet infrastructure, faked transaction data and triggered the exchange’s authorization process, CEO Gracy Chen said on X. She said Bitget’s private keys were not compromised.
The distinction limits the scope of the breach. Stolen private keys can let an attacker continue signing transactions, while Bitget said it has contained the outflow and blocked any further unauthorized transfers.
Bitget first detected unauthorized transfers from some of its hot wallets at 18:31 UTC on Sept. 24. The breach also reached its warm-wallet layer, which sits between internet-connected hot wallets and offline cold storage.
The exchange’s cold wallets remained secure, according to Chen. The exact method used to enter the system is still under investigation, and Bitget plans to release a full technical report once the findings are confirmed.
Chen said Bitget’s User Protection Fund holds more than $464 million and will cover the entire loss. She also said customer account balances remain accurate and user assets are protected.
Deposits and trading remain available, but Bitget has paused withdrawals while it conducts a security review. The exchange has not provided a timeline for restoring withdrawal access.
Multiple technical teams are working on remediation and additional security measures, Chen said. Bitget plans to announce a withdrawal timeline once it can provide one with confidence.